Owner-controlled Zero Trust to secure your critical sites and assets
Faction delivers enterprise-grade Zero Trust at a fraction of the cost of Enterprise SDN or ZTNA — protecting your vulnerable OT & IoT, data, and communications without rip-and-replace
You keep the power on, the water flowing, the service running — often with a lean team and a tight budget. The systems you depend on are spread across substations, field sites, and remote assets, and almost all of them are now connected. That connectivity is exactly what attackers are counting on, and the shift to renewables — distributed solar, storage, and EV infrastructure that has to be reachable to work — only widens the opening.
This isn't theoretical, and it isn't only about stolen data. U.S. agencies have warned that state-sponsored actors — the campaign known as Volt Typhoon — have quietly pre-positioned inside grid, water, and pipeline networks so they can disrupt service in a crisis. At the same time, the FCC has determined that the foreign-made routers in countless sites pose an unacceptable national-security risk. The hardware you already run may be part of the problem.
Lost service & revenue
Every hour of downtime is lost revenue — and, for many utilities, penalties on top of it.
Recovery costs
Incident response, equipment replacement, and overtime a lean operation can't easily absorb.
Customer trust
Outages and breaches make the local news — and erode the confidence your customers place in you.
Regulatory exposure
NERC CIP obligations carry real penalties for non-compliance.
Networking
- Field assets that must stay connected — and are reachable from the public internet today
- The same 'living off the land' paths nation-state actors like Volt Typhoon use to hide in normal traffic
- Foreign-made networking hardware now flagged as a national-security risk, already in your sites
- Coordinating securely across the operators and vendors who jointly run the infrastructure
Devices
- Decades-old PLCs, RTUs, and control systems that can't be patched
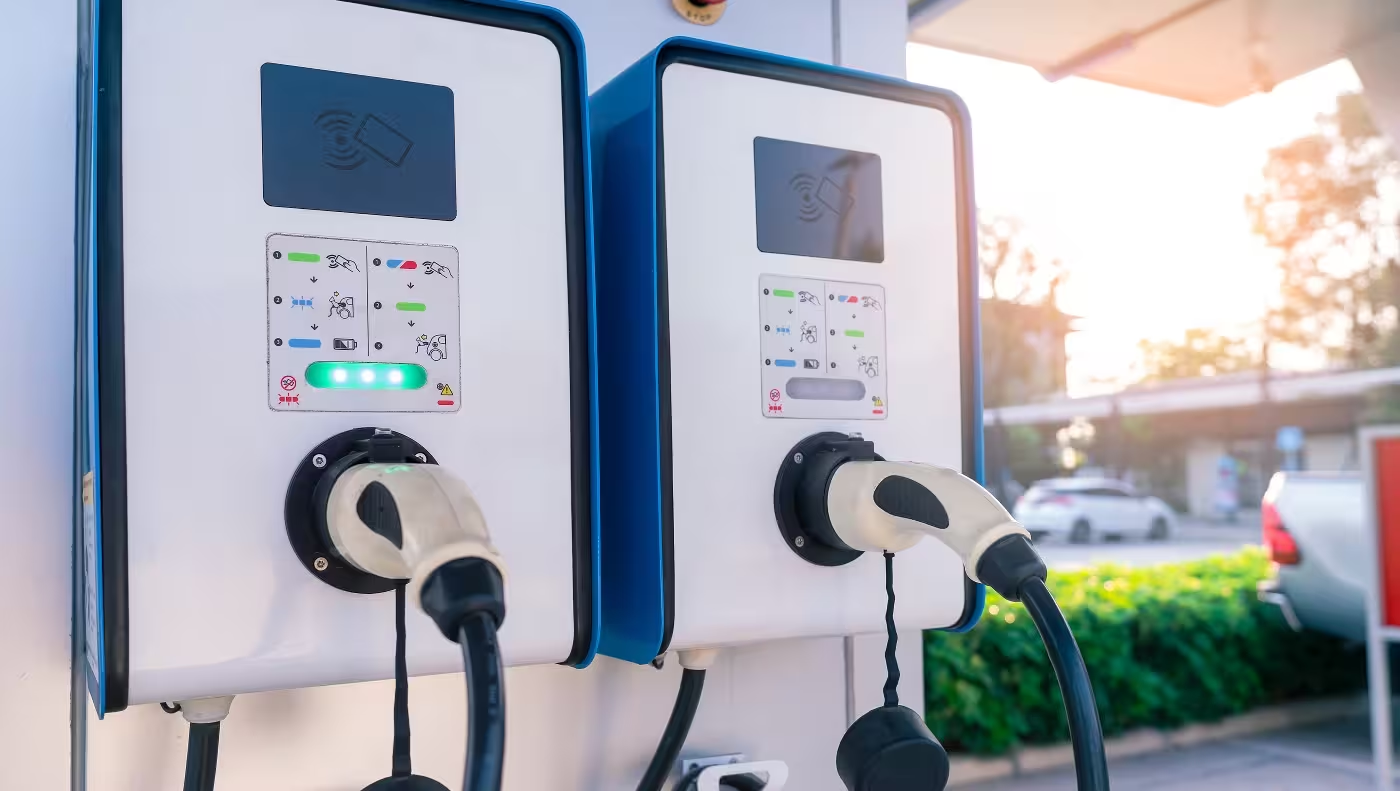
- Distributed field assets — chargers, batteries, solar inverters, sensors
- Everyday smart hardware already inside your network — printers, cameras, UPS — routinely used as a way in
- Cloud application servers that control field devices
Data
- Operational data and field telemetry that can be manipulated in transit
- Communications between the independent parties that must collaborate
- Records compliance requires you to store and share
- Data downloaded onto vendor and staff BYOD devices
Virtual Private Circuit (VPC)
Take chargers, batteries, sensors, control systems — and the application servers that manage them — off the public internet into a circuit only your organization can see and reach. Segment and micro-segment it with Groups, so generation, distribution, and operations stay isolated.
- Sites, substations, and operations on one circuit
- Control systems reachable only from inside
- Identity-based access between segments
- No shared cloud control plane to compromise
Owner-Controlled Keys & Zero Knowledge
Encryption keys are created and held by you and never leave your devices. Faction routes traffic but has no access to what you protect.
- Field telemetry encrypted end to end
- Keys stay with the operator
- Encrypted in transit and at rest
- No vendor in your trust path
Zero Trust, Identity-Based Access
Every user and device is authenticated and authorized; nothing anonymous can reach the circuit. Scope and revoke access for the many vendors who touch field assets.
- Out-of-band Zero Trust authentication
- Time-limited, scoped vendor access with audit trails
- Step-up to verified human identity (iValt, roadmap)
- No anonymous movement on the network
Cyber-Assured Hardware — Pods & Portals
Faction's own purpose-built, Cyber-Assured networking hardware brings remote and legacy field assets into the circuit with no agent — and is trusted hardware by design, a direct answer to the foreign hardware now flagged by the FCC.
- Reach charging stations, solar, batteries, and sensors
- No agent, no patching of the device
- US-made, independently source-inspected
- Built for distributed, unmanned sites
Encrypted Data & Ransomware-Proof Backup
The Faction Data Security Suite keeps files, email, and media encrypted under your keys — and backs them up where only you can decrypt them.
- Keep the email and cloud tools teams already use
- Every file encrypted under your own keys
- Owner-keyed backup that can't be ransomed
- Share with partners without exposing operations
Secure the infrastructure you already have — don't rip and replace it
So what do you do about the foreign-made routers on the FCC's Covered List, or the decades-old gear that Volt Typhoon–style attackers look for? Ripping out and replacing working infrastructure is slow, expensive, and disruptive — exactly what a lean operation can't afford.
Deploying a Faction Virtual Private Circuit is the faster, lower-cost path. You secure the machines and devices that matter by choosing from three flexible options — Faction Pods and Portals, Faction Outposts, or hardware you already own enabled with Canopy — and you can pick one or mix and match.
- Secure existing networking hardware in place rather than replacing it.
- Replace only what can't be brought up to standard — with Cyber-Assured Pods & Portals.
- No multi-quarter rip-and-replace project and no service interruption.
- Reach Zero Trust on your timeline and budget.
Bring everything from PLCs to IP cameras onto your owner-controlled network — reachable by what you need, unreachable from the public Internet. No agents, minimal IT support, no rip-and-replace.
Supports your NERC CIP program
Cryptographic isolation, owner-controlled keys, and identity-based access map directly to the standards utilities answer to. Faction supports your compliance program across the CIP requirements that matter most:
Electronic security perimeters and cryptographic isolation — your systems sit off the public internet by default.
Systems security management — block unauthorized access without modifying sensitive legacy systems.
Information protection — encrypt operational data and control-center communications under your own keys.
Supply-chain risk — scope and time-limit vendor access, with full audit trails.
Internal network security monitoring — meet the emerging requirement as deadlines approach.
Foreign-made routers pose clear risks and should be assessed for replacement or reconfiguration. Deploy a Faction Pod, Portal or Outpost, or bring hardware you already own under Faction protection with Canopy, to reduce exposure without rip-and-replace.


Own your trust. Keep your peace of mind.
The new threat environment calls for a new Zero Trust model. We'd welcome the chance to show you how Faction puts you in control and secures your critical systems and assets rapidly with low cost and IT overhead.